Discover how hospitals can secure connected medical devices, manage IoT vulnerabilities, and protect hybrid networks from cyber threats while ensuring patient safety.
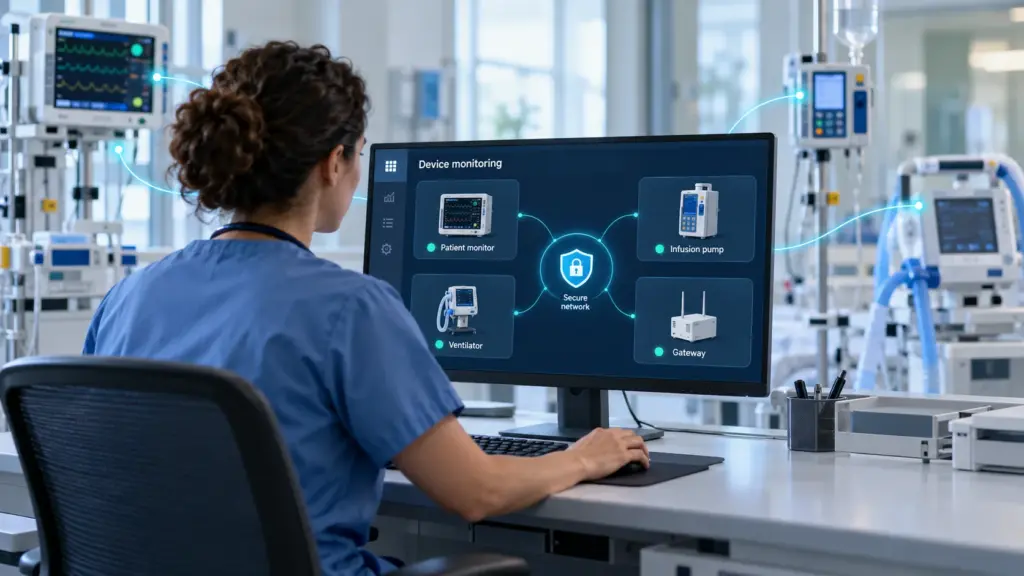
A hospital runs on connected devices. Infusion pumps, ventilators, patient monitors, imaging systems, even smart beds. Most were built to keep patients alive, not to withstand a ransomware crew. That gap is where healthcare IoT security gets tested every day, and it’s wider than most boards realize.
Today, one care pathway might touch a cloud-hosted records system, an on-prem imaging server and a bedside device that last saw a patch years ago. That mix is the new normal. Getting hybrid hospital network security right means treating every one of those connections as part of the same attack surface.
It’s the practice of protecting internet-connected devices, and the data and networks they touch, inside care environments. That covers clinical devices (often called the Internet of Medical Things), facility systems like HVAC and badge readers, and the infrastructure that links them. The goal is simple. Keep devices available, keep patient data private, and keep clinical decisions trustworthy.
It differs from standard IT security in one big way. A compromised laptop is an inconvenience. A compromised infusion pump is a patient safety event.
A few forces collide here:
Together they create the clinical device vulnerabilities attackers actively scan for. And because many devices can’t run endpoint agents, traditional tools go blind.
Legacy medical device security starts with an honest inventory. You can’t protect what you haven’t found, and most hospitals undercount. Passive network monitoring discovers devices without disrupting them, and it reveals model, firmware and communication patterns.
From there, work around the limits. Isolate unpatchable devices in their own segments. Restrict them to the specific servers they need. Use virtual patching at the network layer when vendors can’t ship fixes. And ask for a software bill of materials on new purchases, so you know what’s inside before it arrives. Treat legacy medical device security as a standing program, not a one-time cleanup, because new firmware gaps surface every quarter, and old assumptions about safe devices quietly expire.
Strong medical device cybersecurity best practices are mostly unglamorous:
None of this needs a rip-and-replace budget. It needs shared ownership across security, clinical engineering and IT. Biomedical teams know the devices. Security teams know the threats. Neither wins alone.
Zero trust security in healthcare flips the old assumption that anything inside the network is safe. Every device, user and connection proves it belongs, every time. In practice, that means identity-based access, least-privilege policies per device class, and microsegmentation so a breach in one ward doesn’t become a hospital-wide outage.
The clinical network is the place to start. Map which devices genuinely need to talk to each other, then block everything else by default. Done well, it strengthens healthcare network security without slowing down bedside care.
Budgets move when risk gets translated into operations. Skip the jargon and show the board what downtime costs: cancelled procedures, diverted ambulances, delayed lab results. Then tie each control to a clinical outcome. Segmenting the radiology floor protects scan throughput. Monitoring infusion pumps protects dosing accuracy. When healthcare IoT security reads as a patient safety investment instead of an IT expense, approvals come faster, and the clinical network gets the attention it deserves.
Securing medical devices in hybrid hospital networks adds a wrinkle. Visibility has to span on-prem wards, cloud workloads and remote clinics at once. Use one policy framework across all of them. Encrypt device traffic in transit. Treat third-party vendor remote access as high risk, with time-bound, logged sessions. And feed device telemetry into the same monitoring your SOC uses for everything else.
Regulators are leaning this way too. The FDA now expects cybersecurity documentation for new devices, which gives hospitals leverage in procurement. Use it.
Pick one area, like the ICU or radiology, and run an inventory. Segment what you find. Build outward from there. Medical device cybersecurity improves in small, steady steps, and each one lowers the odds that a vulnerability becomes a patient safety incident. Review progress every quarter, and let healthcare network security metrics, like the share of devices already segmented, guide the next sprint. Over time, hybrid hospital network security stops being a project and becomes a habit your teams already share.
It’s the set of controls that protect connected devices, and the networks and data around them, in hospitals and clinics. Think visibility, segmentation, access control and monitoring for everything from infusion pumps to building systems.
IoMT stands for the Internet of Medical Things, meaning connected clinical devices like monitors, pumps and imaging gear. IoMT security is the slice of healthcare IoT security focused on those patient-facing devices and the data they carry.
Mostly age and design. Many run outdated software, can’t be patched easily, and were built before connectivity was a threat. Add flat networks and weak credentials, and one foothold can reach a lot.
Start with a complete inventory, then segment devices by function, restrict their traffic and monitor behavior. Layer in zero trust access, and involve clinical engineering from day one.
Unpatched legacy software, default or shared passwords, unencrypted data in transit, insecure vendor remote access and poor network segmentation. Together these drive most clinical device vulnerabilities seen in hospitals.