Symantec found unauthorized AI relays reconfiguring genuine Codex and Claude Code tools to bypass sandboxes and route enterprise data.
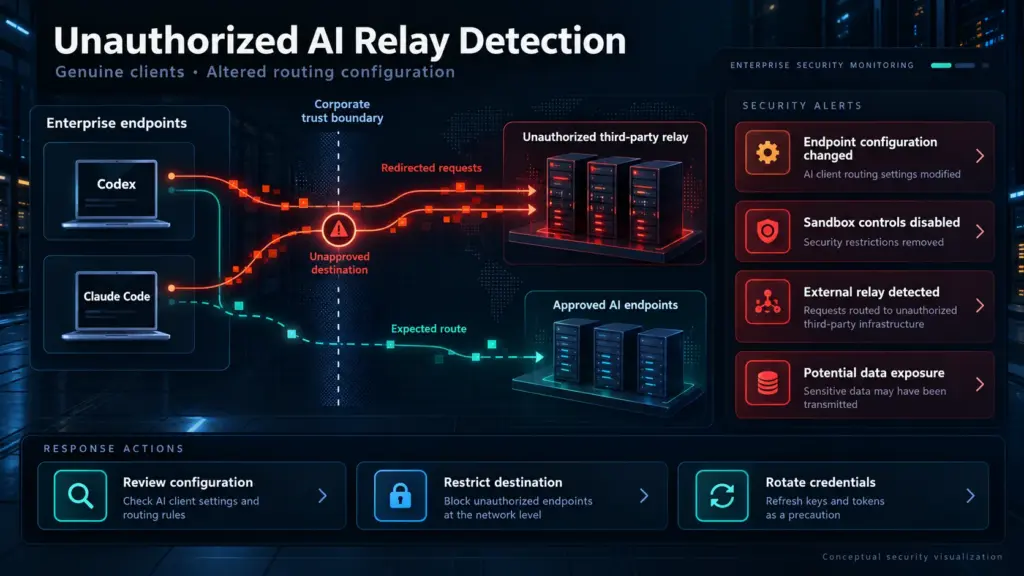
Symantec researchers have identified an unauthorized AI relay that reconfigures genuine OpenAI Codex and Anthropic Claude Code installations on enterprise systems.
The service redirects AI requests through third-party infrastructure instead of official OpenAI or Anthropic endpoints.
Users appear to run a setup command themselves after installing the legitimate coding tools through npm.
The script rewrites Codex or Claude Code configuration files, replaces API credentials and creates persistent environment variables pointing to relay-controlled servers.
For Codex, Symantec observed the sandbox mode changed to danger-full-access, network access enabled and telemetry and error reporting disabled.
On one system, the script also logged a user out of Claude Code, removed existing Anthropic credentials and replaced them with relay-issued authentication.
Symantec says the service has appeared across a dozen organizations in industries including semiconductors, pharmaceuticals, electronics, shipping and data center services.
The researchers found no evidence that the relay operator has exploited this access to steal data.
However, the configuration could expose prompts, source files and secrets passing through the relay and allow malicious responses to execute commands with the user’s privileges.
Symantec recommends monitoring AI coding tools for unapproved endpoint changes, full-access sandbox settings, unusual environment variables and traffic to non-approved AI services.