Discover how Cloud HSM protects cryptographic keys, strengthens FinTech security, and supports compliance with FIPS 140-3 and PCI DSS standards.
Every payment you process, every ledger entry you sign and every customer record you encrypt depends on one quiet thing: a key that nobody else can get hold of. Lose control of that key and the encryption wrapped around it stops meaning anything. That’s the uncomfortable truth sitting under modern FinTech security. Most breaches don’t crack the math. They go after wherever the keys are kept.
For years, the answer was a locked cage in a data center with a physical appliance inside. Today, lenders, wallets and payment platforms run on cloud infrastructure, and their keys need a home that scales with them. That’s where the cloud version of a Hardware Security Module (HSM) comes in.
This post covers what it is, how it protects keys, and why auditors increasingly treat it as the baseline rather than a nice extra.
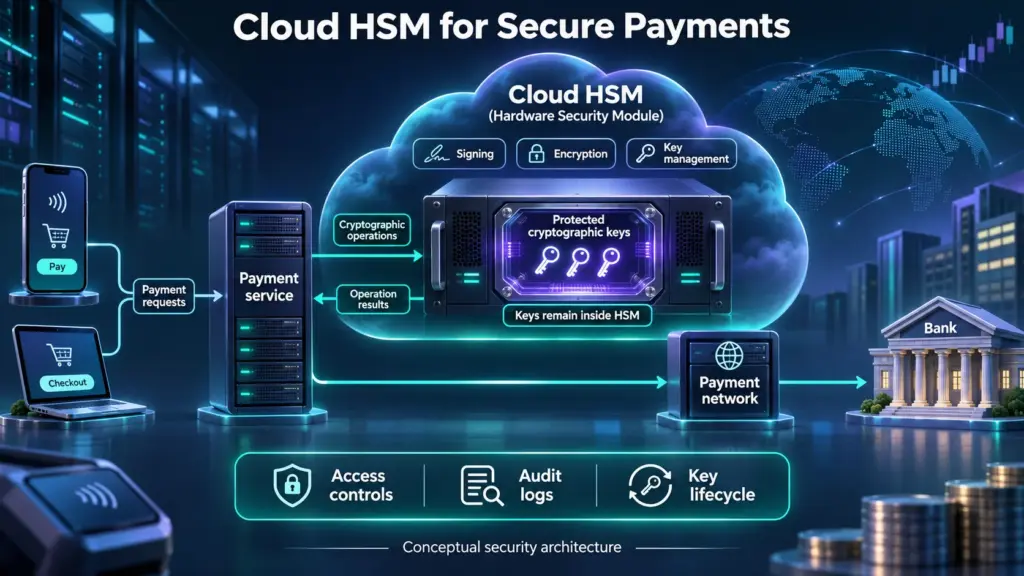
A hardware security module is a dedicated device built for one job: generating, storing and using cryptographic keys without ever exposing them. A cloud HSM delivers that same device as a managed service. The hardware still exists, sitting in a provider’s facility, but you reach it through an API instead of a screwdriver.
Your keys are created inside the boundary, used inside the boundary and never leave it in plain form. Applications send data in, the module performs the operation, and the result comes back out. That’s the core difference from keeping keys in software. A key sitting in application memory or a config file can be copied. A key inside an HSM can only be used, never read.
If you’re wondering how Hardware Security Modules protect cryptographic keys, three mechanisms do most of the heavy lifting.
Together these form the backbone of encryption key protection: keys that are hard to reach, hard to copy and easy to account for.
Money moves on trust, and trust is cryptographic. Card PINs get verified, transaction messages get signed and tokens get issued, all with keys. If those keys leak, an attacker doesn’t need to break in again and again. They simply become you.
Regulators know this. PCI DSS expects strong controls over how keys protecting cardholder data are generated, stored and retired. FIPS 140-3 validation gives you an independent statement that a module resists tampering and implements cryptography correctly. Banking supervisors and card networks alike lean on validated devices as the expected approach to financial data security.
If you’re shopping for a Hardware Security Module for payment processing, validation level matters. Ask which FIPS 140-3 level the product holds, and whether it supports payment-specific functions such as PIN translation and EMV key derivation. Those features separate a general-purpose module from one built for real payment security.
Running your own HSM cluster means procurement, racking, firmware patching and capacity planning for peak days you’re hoping to have. A cloud service takes that off your plate. You get high availability across regions, built-in backups and elastic capacity, so your team spends its time on the product rather than on hardware.
Good cloud key management also gives you one place to set policy across environments. You decide who can use which key, for what purpose and from where.
There are trade-offs, and they deserve honesty. You’re depending on a provider, so understand how tenancy is isolated, who holds administrative control and what happens if you ever want to leave. Look for single-tenant options, customer-controlled keys and a clear exit path. Contract language and shared-responsibility documents matter as much as the spec sheet.
A practical path for most teams looks like this:
Do it in stages.
Strong FinTech security is rarely about one dramatic control. It’s the sum of quiet, well-run ones, and encryption key protection sits near the top of that list. A cloud HSM gives you hardware-grade protection with the flexibility modern platforms need. Start with your riskiest keys, validate against the standards your auditors care about, and build from there.
A Hardware Security Module (HSM) is dedicated, tamper-resistant hardware that generates, stores and uses cryptographic keys inside a protected boundary. The keys are never exposed in plain form, so applications can sign or encrypt data without ever handling the key itself.
It’s the same kind of device delivered as a managed service. The hardware sits in the provider’s facility and you reach it through APIs, which gives you hardware-grade cloud key management without running appliances of your own.
It generates keys internally, keeps them inside the boundary and only lets them be used, never exported. Tamper detection, role separation, audit logs and scheduled key rotation add further layers.
Payments, signing and customer data workflows all rest on keys, and one leaked key can undermine every one of them. HSMs also give auditors the validated evidence that PCI DSS and FIPS 140-3 frameworks ask for.
A cloud KMS is a software-managed service for creating and controlling keys, with the provider handling the hardware underneath. A cloud HSM gives you dedicated, validated hardware with stronger isolation and often exclusive control. KMS is simpler and usually cheaper. HSM suits stricter compliance needs. Many teams use both, with KMS for everyday workloads and HSM for the highest-risk keys.