Learn how AI agent governance helps enterprises manage custom AI assistants, control access, monitor risks, enforce policies, and improve AI oversight.
Somewhere in your company, a finance analyst has built a small assistant that reads vendor contracts and drafts the summaries she used to write by hand. It works. It gives her back most of a Thursday. Nobody in IT knows it exists, and nobody has checked what it can reach inside the document store.
That is where a lot of enterprises are sitting right now. The pilots went well, teams got ambitious, and assistants spread sideways through departments faster than any approval process could follow them. The encouraging part is that you do not have to pull any of it back to get control. You need an inventory, a named human attached to every entry, and a review you actually hold.
AI agent governance is the set of practices that decide which autonomous assistants are allowed to run inside your organisation, what systems and data they can reach, who answers for their behaviour, and when they get switched off. Approval, documentation, permissions, monitoring, retirement. That is the whole scope.
It sits beside model governance rather than inside it. Model governance asks whether the underlying model is accurate, tested and fairly trained. AI agent management asks something narrower and far more operational: this specific assistant, built by this specific team, holding these credentials, taking these actions at nine on a Tuesday morning. Both questions matter. Only one of them usually has somebody’s name against it, and it tends not to be the second.
Build friction collapsed. A product manager can assemble a working assistant in an afternoon using the same tools she uses to make slides, and she has no reason to think of it as a system going into production. So the same three patterns show up almost everywhere.
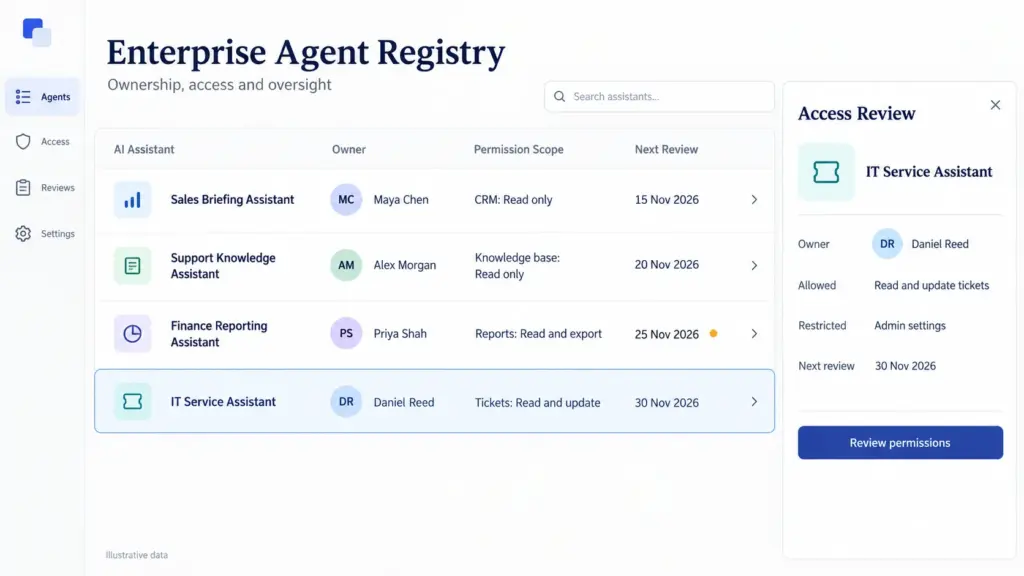
An AI agent registry is a maintained inventory of every assistant operating in your environment, including the ones nobody formally approved. It is the artefact that makes the rest possible, because you cannot govern a population you have never counted.
Ten fields will carry you a long way:
Keep the register boring and easy to find. A spreadsheet that people genuinely update beats a governance platform nobody opens.
Every entry needs one person’s name on it. Agent ownership means a specific human answers for what the assistant does, signs off changes to its instructions, and gets called when it behaves strangely. Not a team alias. Not a distribution list. A person, with a deputy named underneath them so holidays do not create gaps.
Access control is where most of the real exposure sits. Give each assistant its own identity instead of letting it borrow a human’s credentials. Scope its permissions to the minimum the job needs rather than the maximum the platform allows. Make sure your logs record which agent took an action, not just whoever happened to set it up. When an auditor asks who opened the compensation folder in March, you want that answer to take a minute.
Handled this way, AI agent management stops being a research exercise and starts looking like identity administration, which your security team already knows how to run.
AI agent lifecycle management treats every assistant as something with a beginning, a working life and an end. Proposal, review, approval, production, monitoring, retirement. Most organisations have the first four and quietly skip the last two.
Give each agent an expiry date at the moment it is approved. Six months for an experiment, a year for anything in production. When the date arrives, the owner either renews it with evidence that it still earns its place, or it gets switched off. Assistants that stopped being useful are the ones most likely to be sitting on stale permissions, because nobody is watching something they no longer use.
Pair that with a light monthly check on the agents with the widest reach, and a deeper quarterly pass across the whole register.
AI agent security is not a separate workstream bolted on at the end. An assistant that reads untrusted input while holding write permissions is a genuinely new category of exposure: instructions buried inside a supplier PDF, a document pulled into a context window and summarised into a channel it should never have touched, credentials left live long after the project closed.
Three things are worth doing early. Treat agents as non-human identities inside the identity management you already run, so they appear in the same joiner, mover and leaver process as your staff. Red-team the assistants with the widest blast radius before the harmless ones. And route anything touching regulated data through whatever Enterprise AI governance forum already exists, rather than inventing a parallel committee that meets twice and then stops.
You can have a working register inside six weeks without a budget line.
Open an amnesty window. Tell every department that anything declared in the next three weeks gets support and no blame, and anything discovered afterwards gets switched off. People come forward when coming forward is cheap.
Capture the ten fields. A spreadsheet holds the first hundred entries comfortably.
Tier by blast radius rather than by how clever the agent is. An assistant drafting internal meeting notes and one with write access to your billing system do not deserve the same scrutiny.
Publish a one-page approval path. If getting an agent approved takes longer than building one, people will carry on building quietly.
Put the review in the calendar with a named chair, not a reminder nobody owns.
Enterprise AI assistants will keep multiplying, and for the most part that is a good thing. A register is what turns AI agent governance into ordinary administration instead of a fire drill you run after something breaks.
Because assistants now act rather than simply answer. They send messages, update records, approve small amounts and read confidential files, all under permissions somebody granted in a hurry. Without governance you cannot say how many are running, what they can reach, or who to call when one misfires. Enterprise AI governance gives you those answers before a regulator or a customer asks for them.
It is a maintained inventory of every assistant in your environment, capturing its purpose, its owner, the systems it connects to, its permission scope, its approval status and its next review date. Everything else rests on it, because you cannot apply a policy to assistants you have never listed.
Most begin with discovery, usually an amnesty period that surfaces whatever already exists. From there they assign a named owner to each agent, narrow permissions to what the job requires, log agent actions separately from human ones, and set review dates that someone is accountable for. Mature AI agent management ends up looking a lot like identity and access administration.
Centralise the standard and distribute the work. One register, one approval path, one set of security requirements, with each department owning the assistants it builds. Risk tiering keeps it proportionate: a light review for low-reach agents, a full assessment for anything touching customer, financial or health data.
It is the practice of managing each assistant from proposal through approval, production, monitoring and retirement. The retirement step is the one people skip and the one that matters most. Agents that outlive their purpose sit on live credentials, and dormant access is where AI agent security problems usually begin.